Enterprise identity security architecture, assessment and authorized testing.
MA Technology Services, LLC is a specialist practice in Microsoft identity security: Active Directory, Microsoft Entra ID and Azure. We design the identity control plane for large enterprises, test it under written authorization, remediate what we find, and build the software that moves device fleets off legacy domains without a reimage.
This site exists as a statement of record. We do not advertise, publish client names, or post research. Work comes by referral.
Practice areas
Scoped, evidence-driven engagements across the Microsoft identity estate. Every finding carries its source, its reproduction and its fix.
Identity security architecture
Design and build of the identity control plane for large enterprises.
- Secure Active Directory domain controller build standards (Windows Server 2019 to 2025), tiered administration and application control lifecycle
- Kerberos hardening, AES enforcement, NTLM detection and removal programs
- Microsoft Entra ID, Conditional Access, Intune and Autopilot architecture for hybrid and cloud-only estates
- Non-human identity governance: service accounts, service principals and managed identities brought under least privilege
Assessment and authorized testing
Independent verification of the estate before and after architecture work.
- Active Directory and Entra ID security assessments against CIS Benchmarks and DISA STIGs, using our own assessment tooling
- Authorized penetration testing and red team exercises against client-owned systems, scoped and authorized in writing
- Kerberoasting, delegation, Active Directory Certificate Services and credential-exposure analysis
- Vulnerability scanning and validation before and after engagements, with director-level remediation plans and risk-acceptance records
Remediation and migration delivery
We stay for the fix, not just the report.
- Phased remediation programs: Group Policy hardening, patch baselines, end-of-life software retirement and vendor coordination
- Active Directory to Entra ID device and identity migration at fleet scale
- Microsoft Sentinel and detection engineering for identity signals
- Runbooks, build standards and evidence packs the client's own team can operate after we leave
How we work
The method is the same whether the deliverable is a build standard, a test report or a product release.
Ground truth over assertion
Every claim is tied to a primary source: the live configuration, the log, the reproduction. If it is not verified, it is labeled unverified.
Assume breach
Architectures are designed for the adversary who already holds a foothold. Tiering, least privilege and detection are requirements, not options.
Authorized, scoped, documented
Offensive work runs only against systems the client owns or holds written authority over, under a signed scope, with full evidence retained.
No exclusions, no shortcuts
Our software is built to run clean under behavioral endpoint detection with zero exclusions. If a control has to be switched off for a tool to work, the tool is wrong.
Private disclosure
Vulnerabilities we find in vendor products go to the vendor through its coordinated disclosure process. We do not publish findings, name targets, or seek credit.
Operable by the client
Deliverables are written so the client's own team can run, audit and extend them without us.
EntraMigrator
Our enterprise software product for moving Windows devices from on-premises Active Directory to Microsoft Entra ID, in place, with the user's profile, applications and management intact.
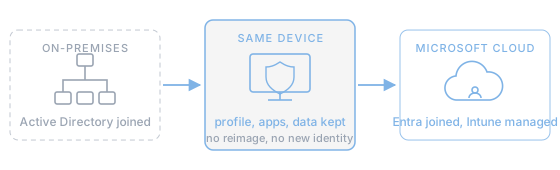
EntraMigrator takes a domain-joined, hybrid-joined or Autopilot-registered device to an Entra-joined, Intune-managed state without a reimage and without creating a second device identity. The migration is driven from a multi-tenant console, delivered by a signed agent, and verified end to end on every device: join continuity across reboots, enrollment with the device credential, profile re-permissioning, and post-join recovery if anything drifts.
It is in production use at large enterprises, including Fortune 500 companies, and is developed, sold and supported directly by MA Technology Services.
Product documentation, security architecture and evaluation access are provided to qualified organizations under NDA.
- Scope
- Active Directory and hybrid-joined Windows devices to Entra ID join and Intune enrollment
- Identity handling
- Reuses the existing Autopilot-associated Entra object; no new device objects
- Delivery
- Tenant-specific signed MSI built from the console; signed agent and catalog
- Security posture
- Runs under Microsoft Defender for Endpoint and CrowdStrike with zero exclusions; signature verification at every code boundary
- Operations
- Fleet lock, arm and re-arm; remote diagnostics bundles; PII-scrubbed migration narration
- Isolation
- Per-customer tenant deployment with isolated control planes
Company
MA Technology Services, LLC is a privately held security architecture and software company based in Sunny Isles Beach, Florida, United States.
Principal
Max Armah, founder and principal architect. Twenty-five years as an enterprise security architect and systems engineer across Fortune 500 financial services, healthcare, utilities, manufacturing and consumer companies, and lead developer of EntraMigrator.
Engagement model
We work directly with enterprise security and infrastructure leadership, and alongside partner consulting practices as the identity security architect of record. Engagements are fixed-scope and written to a decision: what to approve, what to accept, what to retire.
References are available to qualified prospects on request, with the referenced client's consent.
Security contact and disclosure
If you believe you have found a security issue in EntraMigrator or in anything we operate, write to the security contact below. We acknowledge reports promptly and coordinate disclosure with the reporter. Our machine-readable contact file is at /.well-known/security.txt. Published security work on our own products is listed on the security page.
Contact
No forms, no trackers. Email works.
- General
- max@armah.ai
- Security
- max@armah.ai
- Legal entity
- MA Technology Services, LLC
- Location
- Sunny Isles Beach, Florida, United States